> For the complete documentation index, see [llms.txt](https://kunalwalavalkar.gitbook.io/write-ups/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://kunalwalavalkar.gitbook.io/write-ups/bwapp/html-injection-reflected-post.md).

# HTML Injection - Reflected (POST)

## Security level: low

<figure><img src="https://1586847736-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtSZ40gLWhBDTzPEgHsVB%2Fuploads%2FOhycZgw8aPy97XL3urJd%2F1.png?alt=media&amp;token=77f69392-08e4-45fa-9b94-1d74e37e708a" alt=""><figcaption></figcaption></figure>

We are provided with two input fields to input the first and last name.

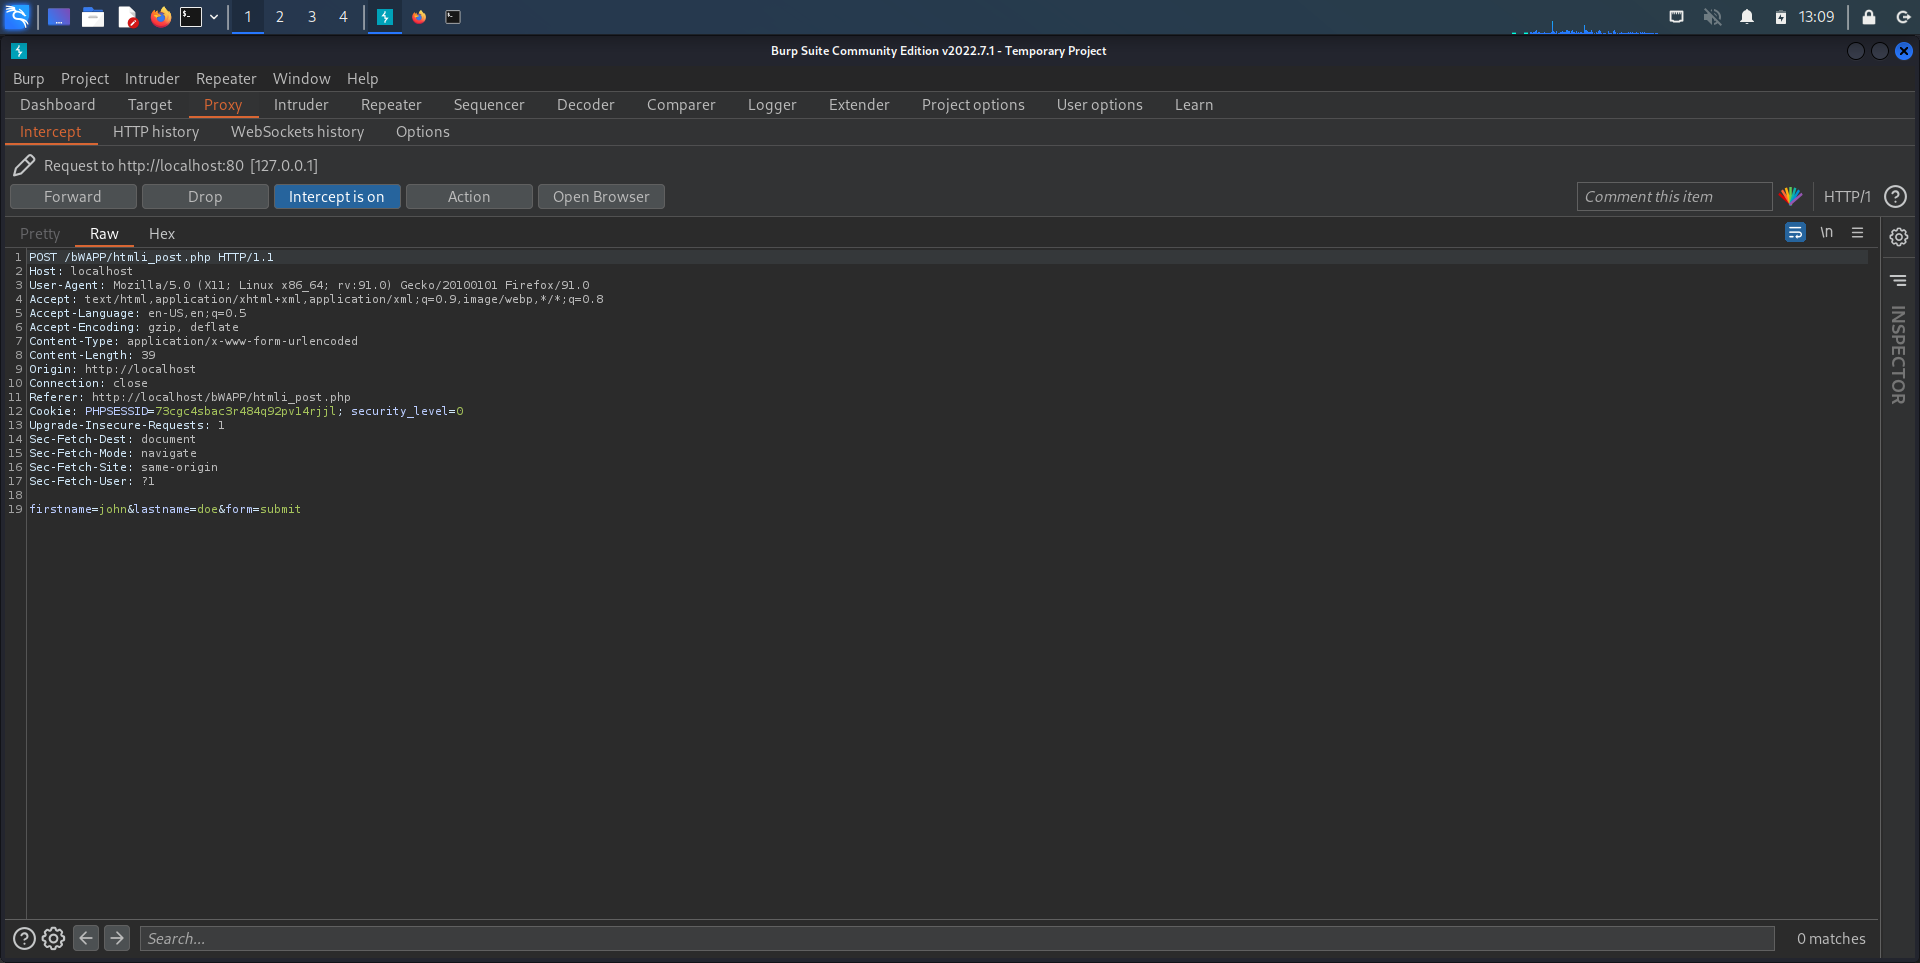
Let's provide the input and intercept the request in Burpsuite.

<figure><img src="https://1586847736-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtSZ40gLWhBDTzPEgHsVB%2Fuploads%2F7MsdF6qYEVuucIGoNg63%2F2.png?alt=media&amp;token=dadc2fdb-f11e-4bb3-a7c5-9e604e3d955c" alt=""><figcaption></figcaption></figure>

We can see that the request method is POST.

Let's input the following HTML tag:

```
First name: 
<h1>john</h1>

Last name: 
<h2>doe</h2>
```

<figure><img src="https://1586847736-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtSZ40gLWhBDTzPEgHsVB%2Fuploads%2FcC85AdP2VozainkSS9hp%2F3.png?alt=media&amp;token=b85e89bd-3b43-4b49-bb9d-2d790cae38bf" alt=""><figcaption></figcaption></figure>

## Security level: medium

Let's intercept the request using Burpsuite.

<figure><img src="https://1586847736-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtSZ40gLWhBDTzPEgHsVB%2Fuploads%2FZDrbY3hw7glU8IX0iiFB%2F4.png?alt=media&amp;token=58cee934-6882-4e44-a232-e8533e094800" alt=""><figcaption></figcaption></figure>

As we can see, our input HTML characters have been URL encoded.

Let's encode the entire input including the name to check if that evades the security filter.

<figure><img src="https://1586847736-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtSZ40gLWhBDTzPEgHsVB%2Fuploads%2Fu5hegJLu5XNmoMzPbBsK%2F5.png?alt=media&amp;token=34fa7605-3cd9-4315-be49-40994a511ce0" alt=""><figcaption></figcaption></figure>

```
firstname:
%3c%68%31%3e%6a%6f%68%6e%3c%2f%68%31%3e

lastname:
%3c%68%32%3e%64%6f%65%3c%2f%68%32%3e
```

<figure><img src="https://1586847736-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FtSZ40gLWhBDTzPEgHsVB%2Fuploads%2Fer24DNQ18ydy4MJimcNj%2F6.png?alt=media&amp;token=f9a1db15-ebdf-47f4-a1c4-8b33296b3f47" alt=""><figcaption></figcaption></figure>

We have successfully exploited the HTML injection vulnerability.